Hodl Hodl has warned Bitcoin traders about phishing emails that impersonate the platform and promote a fake Windows desktop app.
The company said it does not have a desktop app and does not send emails asking users to download software or log in through a link. Anyone who already clicked a link or entered login details should change their Hodl Hodl password and any reused passwords immediately.
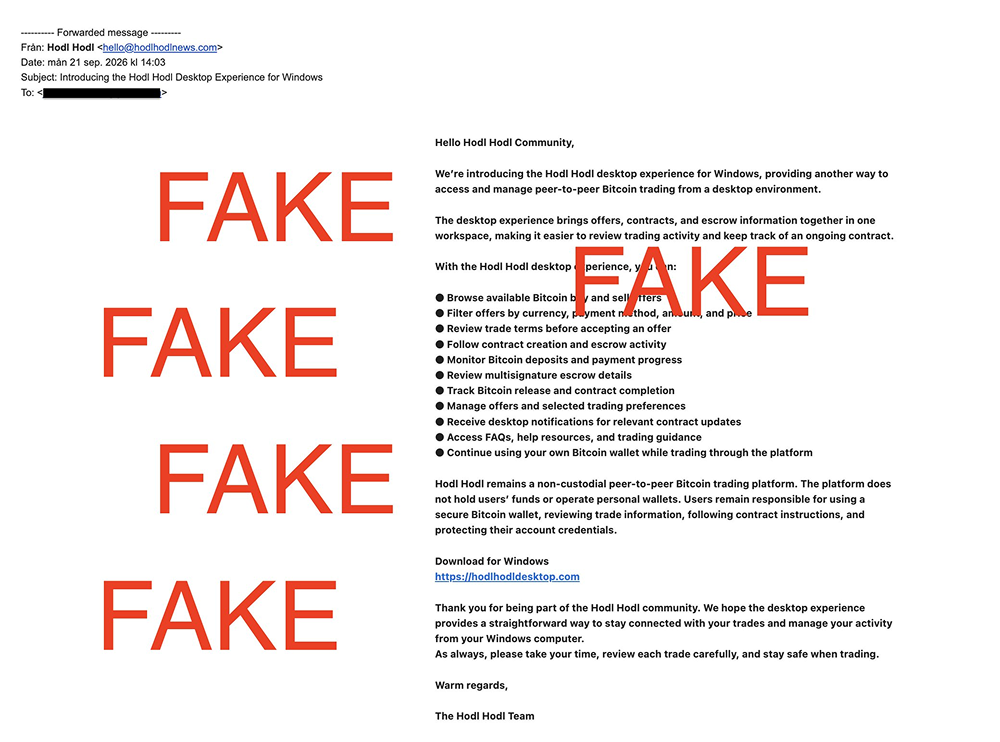
Subject: Introducing the Hodl Hodl Desktop Experience for Windows.
Download link:hodlhodldesktop.com
The message claimed the “desktop experience” would let users browse offers, manage contracts, monitor escrow, and receive notifications from a Windows computer. It also copied Hodl Hodl’s real talking points about non-custodial trading and users keeping their own Bitcoin wallets.
That mix of real product language and a fake download link is what makes the email dangerous.
Hodl Hodl’s official website is hodlhodl.com. Independent reviews also describe the platform as browser-based, with no official desktop or mobile app.
Why this scam is targeting Hodl Hodl users?
Hodl Hodl is a peer-to-peer Bitcoin trading and lending platform. It does not take custody of user funds. Trades use a 2-of-3 multisig escrow setup between buyer, seller, and the platform.
That model is popular with privacy-focused Bitcoin users. It is also a common phishing target because:
Account logins still matter for offers, contracts, and support actions.
Users may expect software tools around trading and escrow.
A fake “new app” can look like a convenience upgrade instead of a scam.
A downloaded file can install malware. A fake login page can steal passwords, 2FA codes, or session data. Either path can put a trading account at risk.
How to tell the email is fake?
Several details give the campaign away:
Hodl Hodl has no desktop app. The company said so directly.
The sender domain is wrong.hodlhodlnews.com is not the company’s official site.
The download domain is wrong.hodlhodldesktop.com is not an official Hodl Hodl domain.
The email asks users to click and log in. Official access should start at the website, not an inbox link.
The timing looks opportunistic. The message is written like a product launch, not a routine account notice.
Official Hodl Hodl channels listed on the company’s contact page include the website, @hodlhodl on X, official Telegram channels, and company emails such as support, dispute, marketing, and security addresses on the hodlhodl.com domain.
What to do if you received the email?
Do this first:
Do not click the download link.
Do not open any attachment.
Do not enter your password, 2FA code, or wallet details.
If you already clicked or logged in:
Change your Hodl Hodl password immediately.
Change any password you reused on other sites.
Review recent account activity, open contracts, and payment details.
Enable or re-check 2FA with an authenticator app, not SMS if you can avoid it.
If you downloaded a file, disconnect the device from important wallets and treat it as potentially compromised.
Report the email to Hodl Hodl through official channels, not by replying to the phishing message.
Hodl Hodl’s advice is simple: only access your account by typing the official website address yourself. Never use a link from email.
Ignore unsolicited “new app,” “security update,” or “verify your account” emails.
Hover over links before clicking and check the real domain.
Use a unique password and a password manager.
Keep 2FA on.
Remember that Hodl Hodl being non-custodial does not make a stolen login harmless. A hijacked account can still interfere with contracts and communication.
Phishing remains one of the most common ways Bitcoin accounts get compromised. The software itself does not have to be hacked if a user is tricked into handing over access.
ENJOYED THIS ARTICLE?Support the authorSend a zap over Lightning or on-chain