Core Lightning Discloses High-Severity Vulnerability That Could Leave Bitcoin Payment Nodes Offline

SECURITY DEVELOPMENT

Vulnerability Could Repeatedly Crash Lightning Nodes

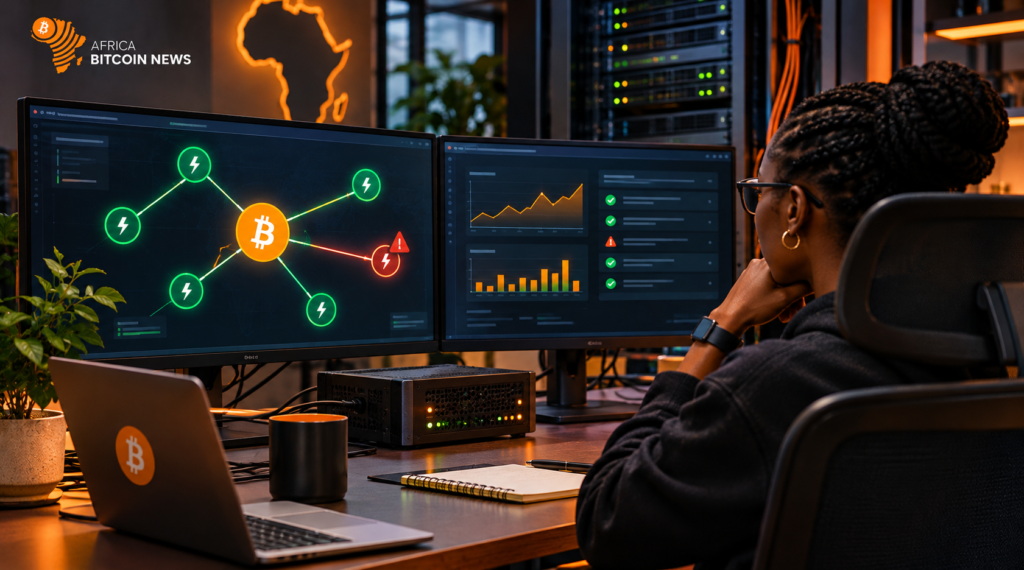
Core Lightning, a software implementation used to operate nodes on Bitcoin’s Lightning Network, has disclosed a high-severity vulnerability that could allow a malicious peer to repeatedly crash an affected node.

The vulnerability, identified as LNF-2026-0004, was publicly disclosed on November 13, 2026, by security researcher Nishant Bansal. It affects Core Lightning versions 0.12.0 through 26.06.7.

The flaw involves how the software handles Bitcoin transaction outputs used to fund Lightning channels. An attacker could reuse an existing funding output to create duplicate channel identifiers, triggering software crashes. In one scenario, the node could enter a persistent crash loop after restarting.
Two Patches Were Needed to Resolve the Issue

The vulnerability had two attack variations. The first allowed an attacker to crash a node by reconnecting after opening a channel with a reused funding output. A second variation involving previously closed channels could leave a node repeatedly crashing on startup.

Developers initially addressed the first issue in Core Lightning v26.06.6, released in July. However, that patch did not cover the closed-channel scenario. A broader fix arrived in version 26.06.8 on September 22, 2026.

The November disclosure is therefore new, but the fixes had already been released. The project’s subsequent v26.06.10 release on November 4 also included additional security fixes and urged operators to upgrade.

What Lightning Node Operators Should Do

The vulnerability matters to businesses, developers and community organisations operating Lightning infrastructure because an offline node cannot reliably process payments or monitor its channels.

The advisory warns that prolonged downtime could expose funds in other channels to risks if a node misses important on-chain events. However, the disclosure does not establish widespread exploitation or confirmed financial losses.

Core Lightning operators should check their installed versions and upgrade to the latest release. The incident also highlights the importance of keeping Bitcoin payment infrastructure updated as security issues are identified and resolved.

ENJOYED THIS ARTICLE?Support the authorSend a zap over Lightning or on-chain